THIS IS TECHNICALLY MALWARE. DO NOT USE THIS ON SYSTEMS OR PEOPLE UNLESS YOU HAVE CONSENT OR IT IS YOUR OWN SYSTEM. USE AT YOUR OWN RISK.
This is a personal cybersecurity project to learn how phishing malware is effective.
If this software were to be packaged as a .jar file and sent to targeted users who are not very tech-literate, this would be an easy way to harvest credentials.
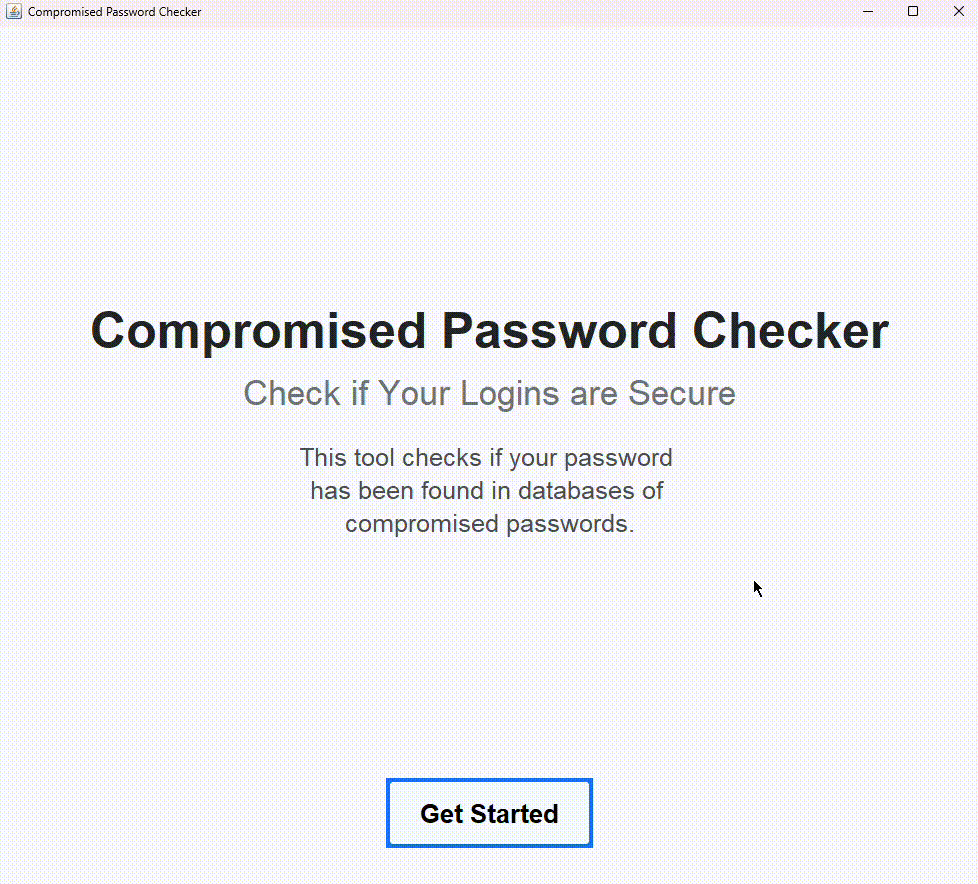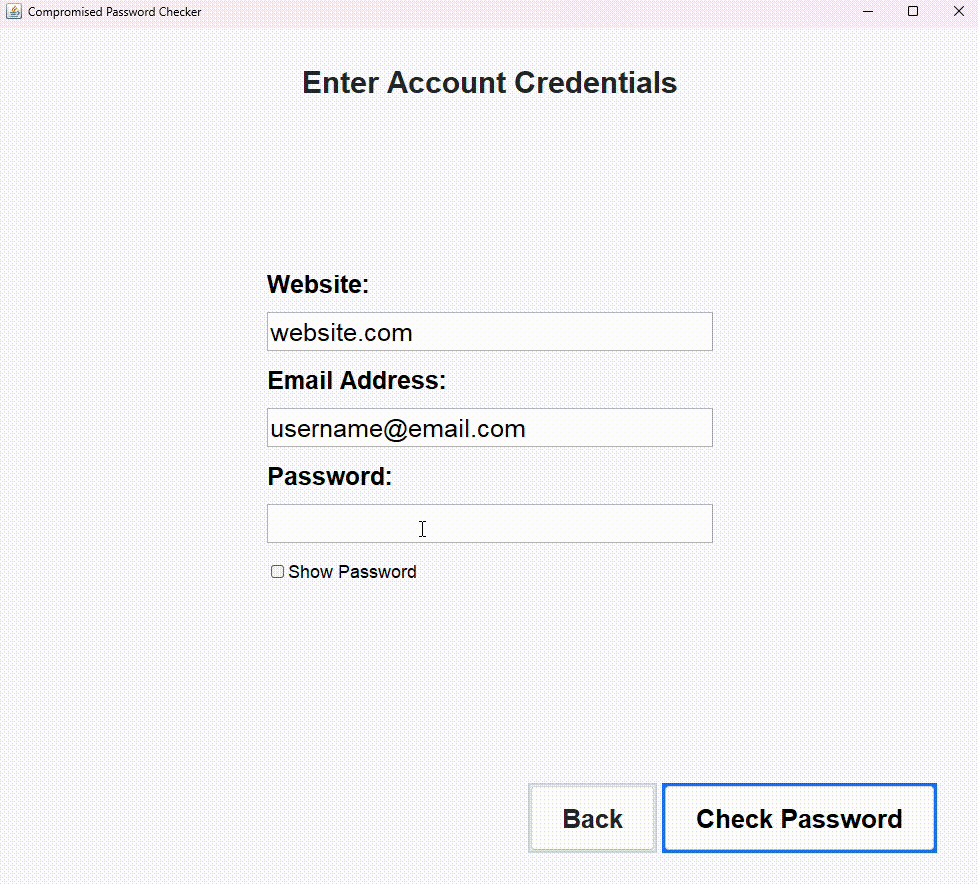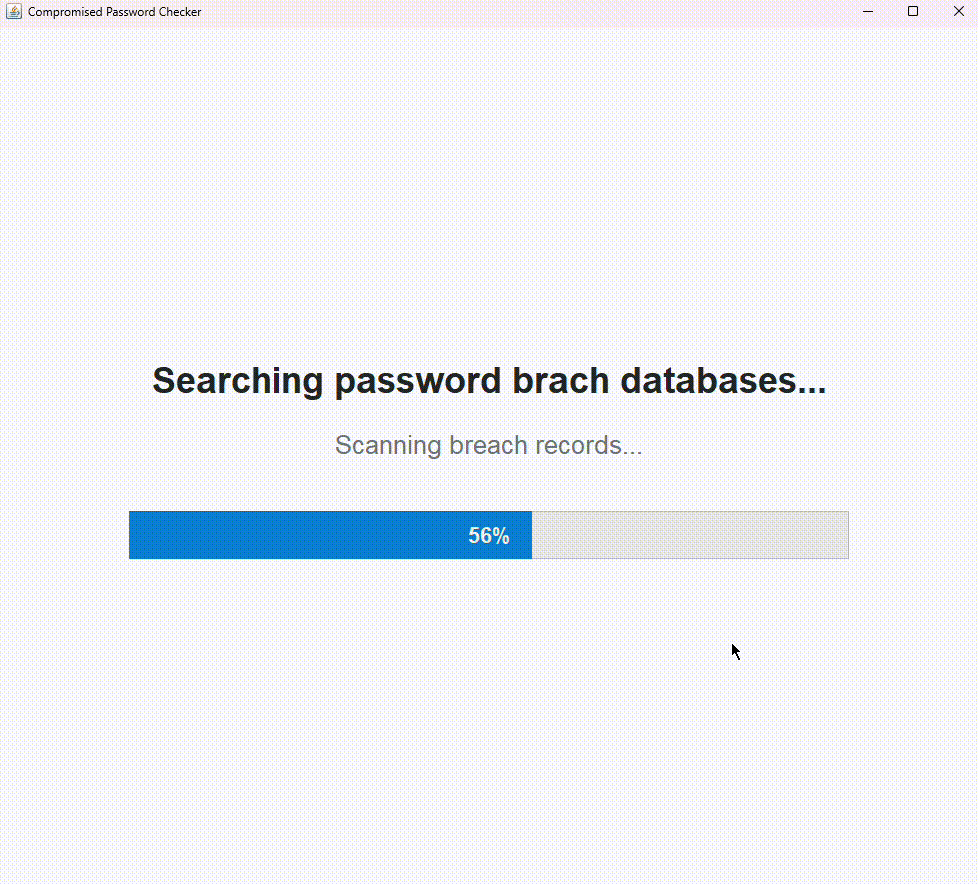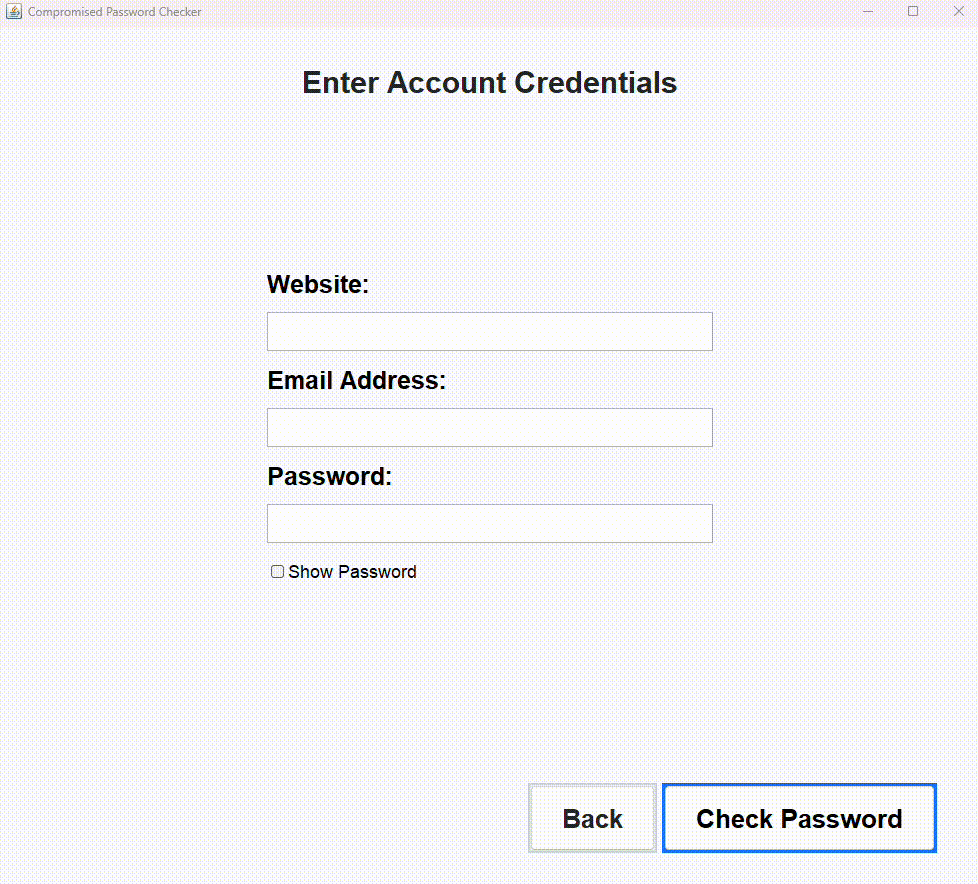
All they would have to do is download and run the file, then fill it out with as many logins as they want to check. Now all those logins are compromised.
If this software would have a way to send the compromimsed credentials over a network connection to an external database server that an attacker manages,
then they attacker could send this malware to many users (through email or other methods) and liklely get a good amount of credentials sent to their database
where they can then go and try to log in to websites and use other methods like social engineering to try and bypass existing login security methods such as Multi-Factor Authentication.
Features:
User-Friendly GUI: Gains trust and comfort from users since its an easy-to-use GUI instead of a CLI application
OS Support: Thanks to this being written in 100% Java, it can run on any OS (Windows, Linux, Mac) as long as it has Java installed
Local Credential Harvesting: Saves credentials to a local "data.txt" file
POSSIBLE FEATURE: Adding network connectivity to this software coulld lead to the harvested credentials being sent to the attacker through various methods, like email, HTTPS, or SSH
Read more and learn how to use/deploy it by visiting the Github Repository.